Key Takeaways
- Plan now and act in waves. The standards are final, the deadlines are set, and large cryptographic transitions take years.
- Start from business risk, prioritizing the applications and data that matter most before connecting them to the cryptography underneath.
- Treat it as an ongoing program. Ownership, governance and continuous discovery matter as much as which algorithms you pick.
- Bring in the whole organization, from IT and application owners to the CIO, GRC, procurement and your vendors.
- Report in business terms so the board can see which business units are quantum-safe and what's still in progress.
Sooner or later every enterprise CISO will need to initiate a post-quantum cryptography migration, and will need a plan. It usually begins as a "migrate everything" mandate, covering keys, certificates, TLS, PKI, code signing and cryptographic libraries, with no obvious starting point and no budget attached. This guide is for the security leader who has to turn that mandate into a program the management and the board can follow. It covers why organizations are planning now, what goes into a workable plan, the phases of the transition, the challenges worth planning around and how to report progress in terms the board understands.
Why CISOs Are Planning PQC Migration Now
Three developments have moved post-quantum cryptography (PQC) off the research agenda and into the operating plan:
- The standards are ready. NIST finalized its first three PQC standards in August 2024, with ML-KEM (FIPS 203) for key establishment and ML-DSA (FIPS 204) and SLH-DSA (FIPS 205) for digital signatures. In October 2026 NIST also finalized its transition plan, NIST IR 8547, which deprecates quantum-vulnerable public-key algorithms after 2030 and disallows them after 2035.
- The deadlines are set. As NIST notes, Executive Order 14412 requires US federal high-value assets and high-impact systems to move to PQC key establishment by 2030 and to PQC signatures by 2031. The EU's Coordinated Implementation Roadmap calls for high-risk use cases to be migrated by the end of 2030, and defense suppliers have CNSA 2.0 to deal with on top of that. Even where these rules don't apply to you directly, they shape what customers, auditors and regulators will expect.
- The market is moving. In 2026, Google and Cloudflare both set 2029 as the target for finishing their own transitions, and major operating systems, browsers and network vendors already ship PQC key exchange, so a growing share of the fix is available off the shelf.
Behind all of this sits the current risk of harvest now, decrypt later (HNDL), where adversaries capture encrypted data today and decrypt it once a capable quantum computer exists, which means data with a long confidentiality life is exposed already. Integrity is at stake too: a capable quantum computer could forge the signatures behind certificates, code signing and software updates. Planning now is simply the proactive choice, since it spreads the cost across several budget cycles and gets the highest-risk systems fixed first.
What Goes Into a PQC Migration Plan
A workable PQC migration plan answers five questions about what you have, what matters most, what you'll fix first, who does the work and how you'll know it's done. In practice that translates into nine components:
- Governance. An executive owner (usually the CISO), a program lead and a steering group. Some organizations formalize this as a Cryptography Center of Excellence (CCoE).
- Business risk model. With applications and data ranked by criticality, sensitivity, confidentiality lifetime and regulatory scope.
- Cryptographic inventory. The cryptography in use across code, cloud, endpoints, PKI and third-party connections, captured in a CBOM (Cryptographic Bill of Materials).
- Prioritization. Scoring each finding on business impact, HNDL exposure, regulatory deadlines and migration complexity.
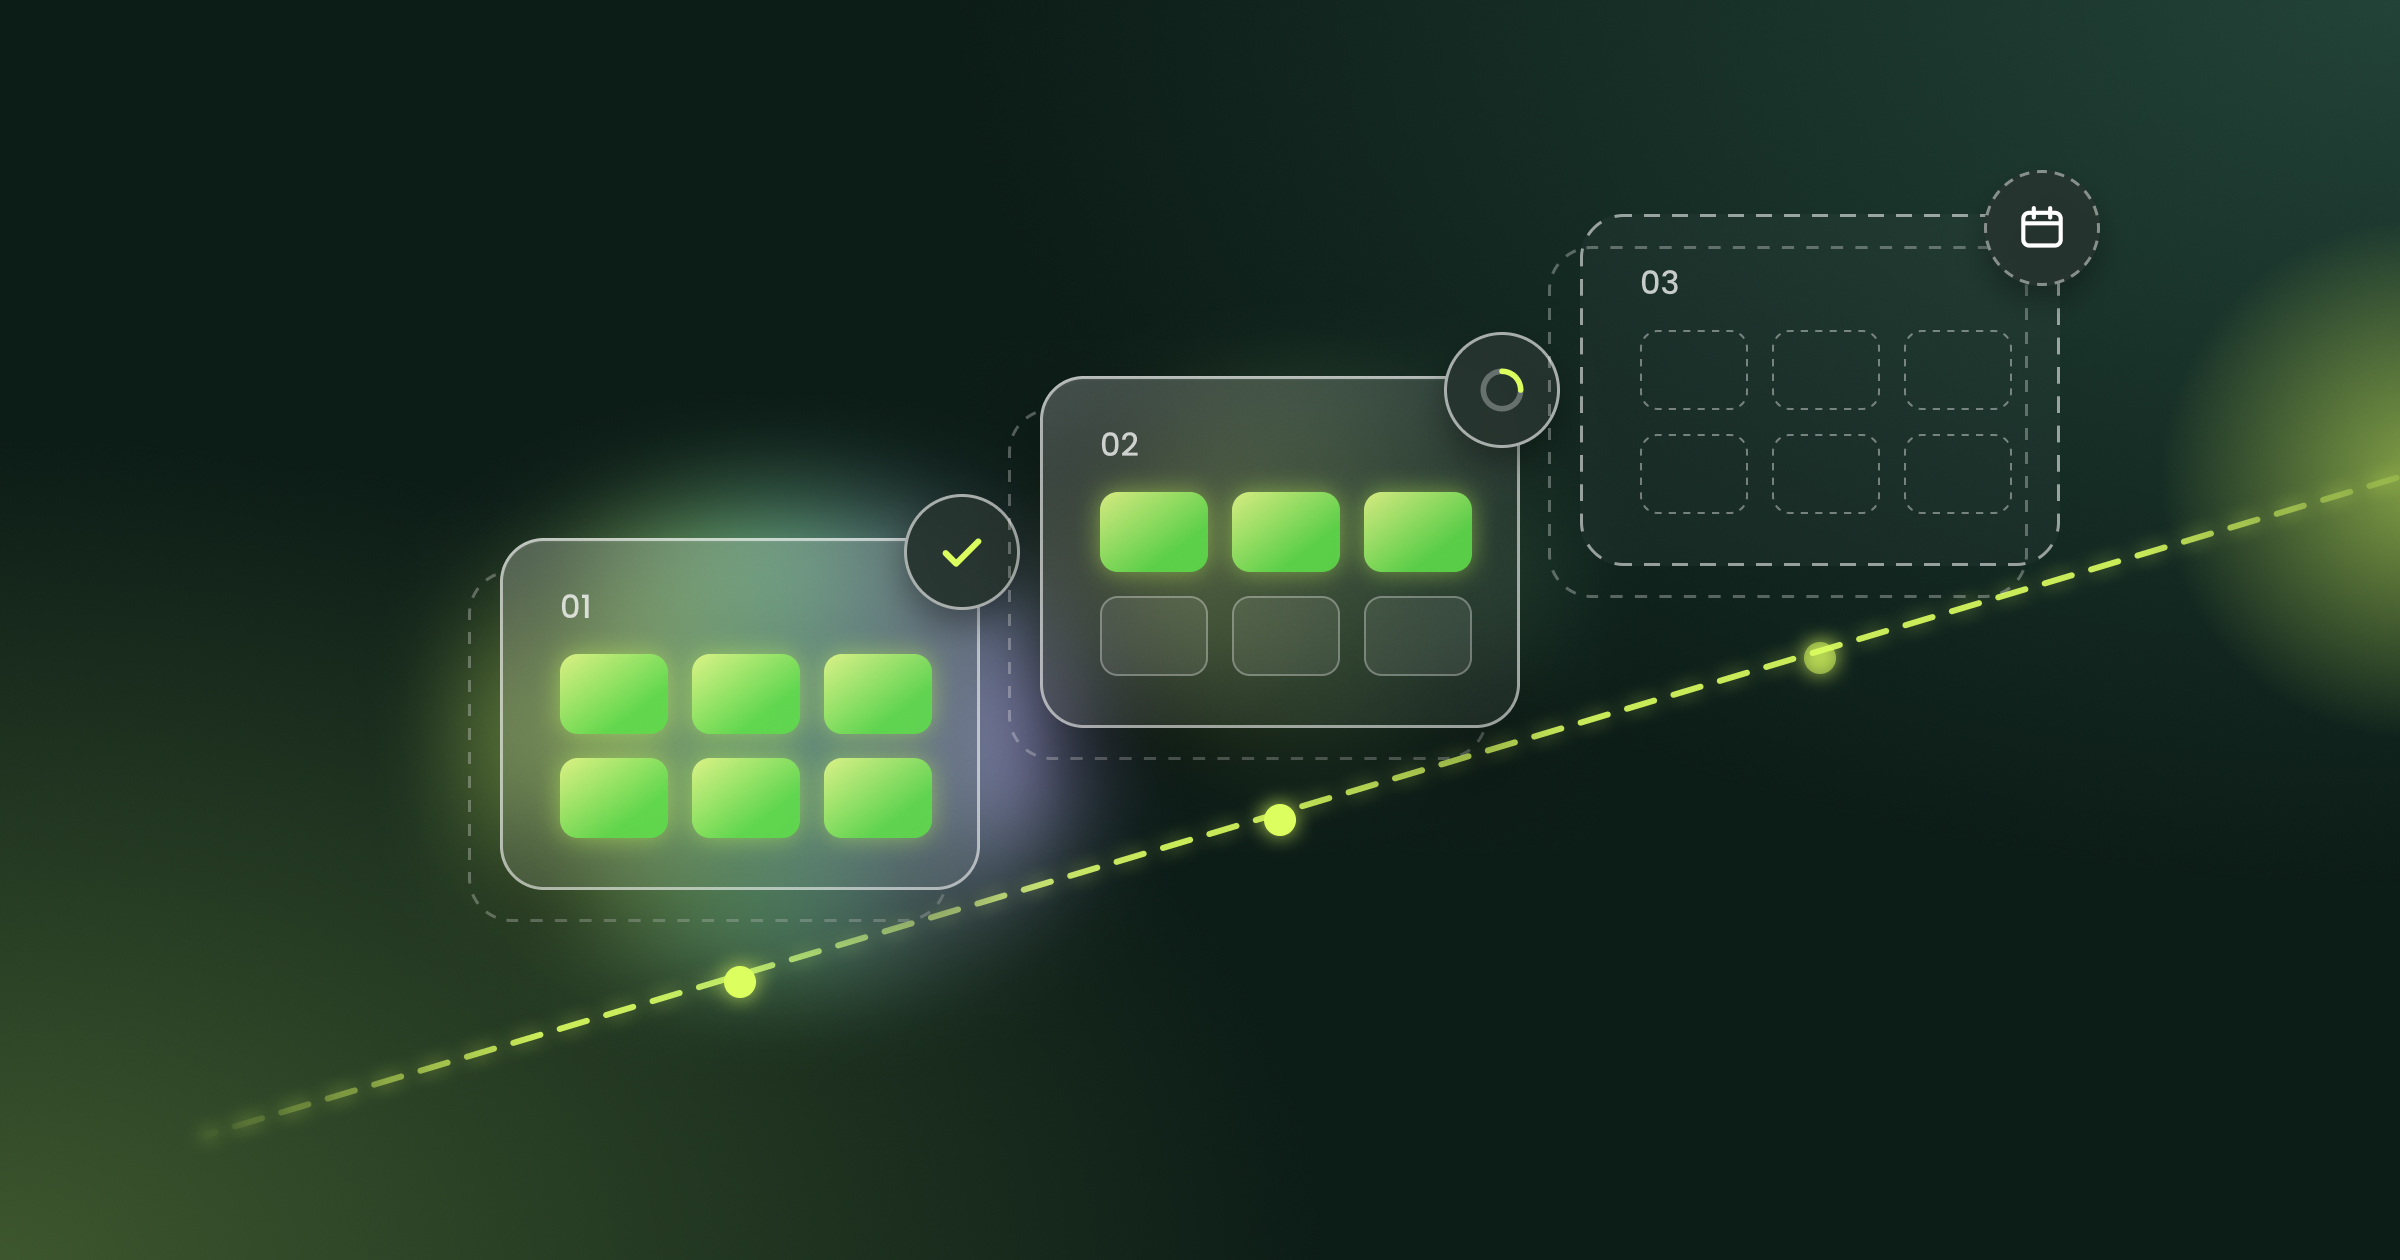
- Phased waves. Time-boxed waves, each with a clear scope, owners, milestones and success criteria.
- Remediation approach. Runbooks, ticketing, change control and validation that proves each fix actually worked.
- Vendor strategy. Supplier PQC roadmaps, with post-quantum readiness written into procurement requirements.
- Budget and resourcing. Phased funding that leadership (typically the CIO) can plan around alongside other IT priorities.
- Reporting. Agreed metrics and a fixed cadence for executives and the board.
Who needs to be involved
Security can't carry this alone, and the plan should name roles for at least these groups:
- The PQC lead or head of crypto-PKI, who runs the program day to day and brings the other groups together
- IT and infrastructure teams, who own servers, networks, PKI and HSMs
- Application owners, who change code and libraries and schedule the releases
- The CIO, who co-owns the budget and has to balance PQC against everything else on the list
- GRC and compliance, who connect the program to regulatory requirements
- Procurement and vendor management, who hold suppliers to their PQC commitments
- Business leaders, who confirm what matters most and accept residual risk
The Phases of a PQC Transition
Most programs follow the same broad shape of discovery, prioritization, remediation and governance. What changes the outcome is what comes first, and starting from business risk even before technical discovery gives every later phase a clear direction.
What a first wave looks like
The first wave sets the tone for the whole program, so keep it small, visible and finishable. A strong first wave usually targets one high-value area, such as a customer-facing application or a business unit with long-lived sensitive data, and runs on a short, fixed timeframe so the team can show a result within a quarter.
It should also end with validated fixes, since a pile of opened tickets proves very little, and it should produce lessons for the next wave, like which libraries were hard to change or which vendors were slow to respond. Over time this builds a recurring rhythm where each wave closes real risk, improves the plan and makes the next one faster.
Two more practical points are worth adding. Start with external data in motion, meaning internet-facing systems and third-party connections that carry long-lived sensitive data, because that's where HNDL risk is highest. Governance should also run as a loop with no real end point, since new code, certificates and vendors appear every week and discovery needs to keep going through cryptographic posture management so new findings feed back into the plan.
Common Challenges in PQC Migration
These are the obstacles CISOs run into most often, along with ways to plan around them.
Most of these share a root cause, which is that the program started with technology instead of with the business. When every task traces back to an application the business cares about, winning budget, assigning owners and keeping teams engaged all get noticeably easier.
Reporting PQC Roadmap Progress
C-level executives and board members want to know whether the organization is on a credible path, what's at risk and which decisions they need to make. Algorithm names rarely help them get there. A good PQC roadmap turns the technical plan into milestones the board can actually follow. Here are a few guidelines:
Frame PQC as a business risk and present it alongside other enterprise risks, with an owner, a target date and a trend line.
Report by business unit and application. A line like "Retail payments is quantum-safe and capital markets are behind plan" tells executives far more than a raw count of migrated certificates.
Use the same metrics every quarter, for example:
- Inventory coverage across in-scope applications
- Quantum-vulnerable exposure, weighted by business impact
- Findings remediated and validated, by wave
- Business units or critical applications that are quantum-safe
- Critical vendors with a committed PQC plan
- Milestones on track, at risk or late
Make the first update a baseline. Show where the organization stands today, which business units are in scope for the first waves and how the plan looks over the next four quarters, and be honest about what's known versus what discovery is still going to uncover.
Connect progress to cost. Pair each milestone with the budget it needs and the risk it removes, which helps the CIO and CFO see PQC as a phased investment with measurable returns.
End with the next decision, whether that's budget for the next wave, a risk acceptance or a push on a vendor that's lagging behind.
Keep it repeatable. Giving the same evidence-backed answer every quarter lets executives see a trend over time, and a PQC readiness baseline at the start gives you the first data point.
Start With Your First Wave
Q.security helps CISOs run PQC remediation as a business-first program, from discovery to done. Start with your public footprint and a few applications, identify your highest priorities and get an actionable plan for your first remediation wave. Talk to Q.security.
FAQ
How long does post-quantum cryptography migration take?
For a large enterprise, expect a multi-year program. The first high-risk systems can be remediated within months, but full coverage takes years because of legacy systems, vendor dependencies and release cycles, and many organizations plan around 2030 for high-risk systems and 2035 for everything else.
Should organizations use hybrid cryptography during the transition?
Often, yes. Hybrid modes combine a classical algorithm with a post-quantum one so a connection stays protected as long as either holds, and NIST accommodates hybrid approaches in its transition guidance. They do add complexity and larger messages, so use them where interoperability needs and risk justify the extra overhead.
Which NIST algorithms replace RSA and ECC?
ML-KEM (FIPS 203) replaces RSA and elliptic-curve key exchange for key establishment. For digital signatures, ML-DSA (FIPS 204) is the main replacement, with SLH-DSA (FIPS 205) as a hash-based alternative, and NIST also picked HQC in 2025 as a backup key-establishment algorithm. Symmetric algorithms such as AES stay in use.